MyID CMS PIV
The US federal edition of MyID® CMS, purpose-built to help agencies, defence contractors and other national governments achieve FIPS 201 compliance. Issue PIV cards, derived credentials and biometric-bound identities at federal assurance levels, on-premise or in air-gapped environments.
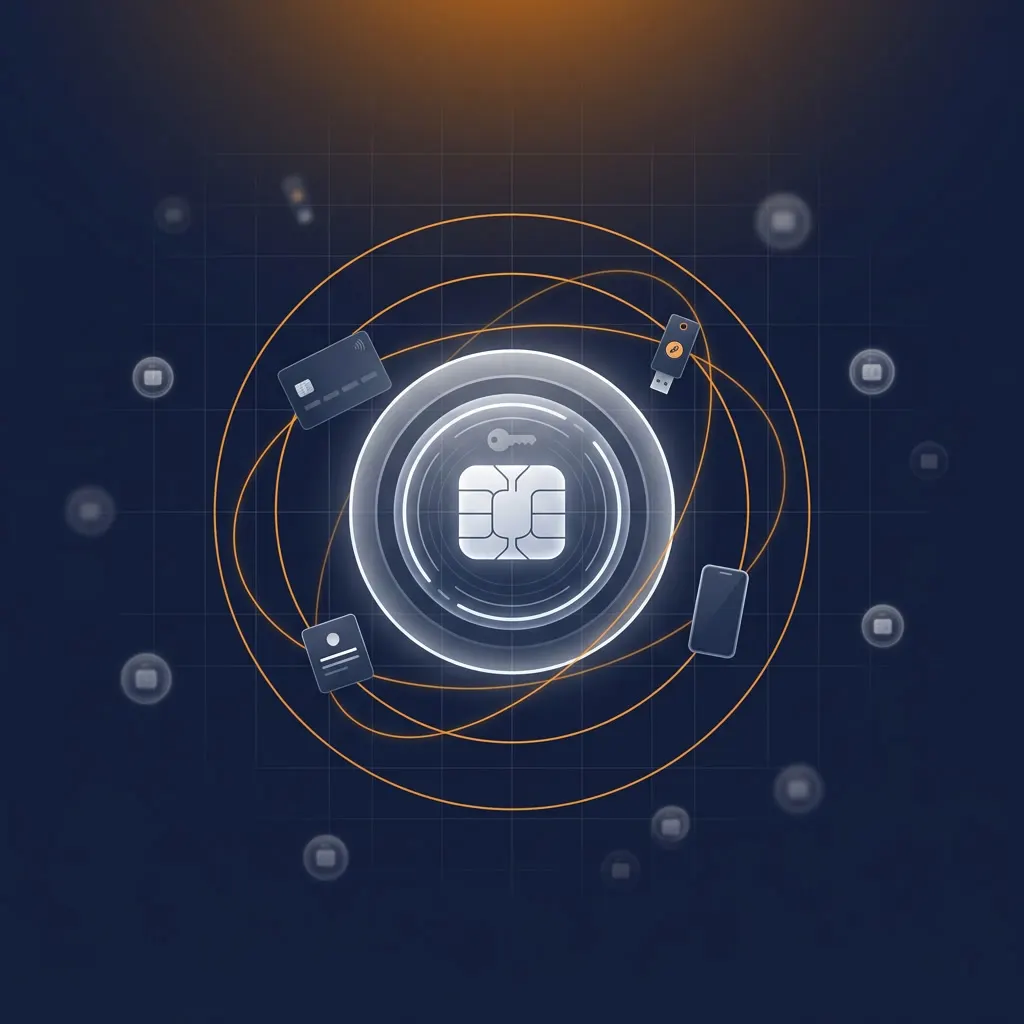
Proven in large-scale federal credentialing deployments
MyID CMS PIV enables national-scale credential programmes for major federal agencies and allied governments, with workforce-scale deployments measured in tens of thousands, hundreds of thousands and into the millions.
A major US federal agency has issued over 81,000 PIV cards and approximately 150,000 certificates across more than 400 locations, with issuance and post-issuance management on MyID.
A national defence organisation runs MyID across multiple air-gapped environments, managing tens of thousands of end-user devices.
Two decades of credential management for US federal agencies, defence organisations and national identity programmes. Trusted in 20+ countries.
Credential management for US federal identity programmes
MyID CMS PIV is the US Federal edition of MyID CMS, engineered specifically for compliance with the FIPS 201 standard. It is deployed at US federal agencies, defence contractors, other national governments and any organisation requiring government-grade PIV credentials.
Aligned with the standards that matter for US federal identity
MyID CMS PIV is built to support the NIST and federal standards that govern Personal Identity Verification. Card personalisation is performed in compliance with SP 800-73, SP 800-76 and SP 800-78.
FIPS 201-3
Personal Identity Verification of Federal Employees and Contractors, latest revision. Logical and physical credentials on one card.
NIST SP 800-73
PIV card data model and interface specification. MyID supports cards that comply with SP 800-73-4, personalised in compliance with the specification.
NIST SP 800-76
Biometric data specification for PIV. Fingerprint capture, facial image capture, conformant templates.
NIST SP 800-78
Cryptographic algorithms and key sizes for PIV. Approved algorithms, validated in deployment.

HSPD-12
Homeland Security Presidential Directive 12. Common identification standard for federal employees and contractors, the foundation of PIV.

Executive Order 14028
Software Bill of Materials (SBOM) and supply chain security. In line with the US Executive Order on Improving the Nation’s Cybersecurity, an SBOM for MyID is available on request to support federal procurement.
Everything a federal credential programme actually needs
Beyond the FIPS 201 baseline, MyID CMS PIV delivers the operational features that real federal credential programmes need on day one.

PIV, PIV-I and CIV on one platform
Issue PIV, PIV-I and CIV credentials from a single MyID installation. PIV-I certificates are issued under a CA cross-certified with the Federal Bridge, so contractors and partner organisations can run federally interoperable credentials.
10-Slap fingerprint enrolment
Full 10-print capture with supported 10-Slap fingerprint readers, including optional fingerprint roll capture. Biometric data is personalised to the card in compliance with NIST SP 800-76.
Fingerprint and facial biometrics
Capture fingerprint and facial biometrics as part of the enrolment process. MyID securely stores biometric templates and includes them within the PIV credential at issuance, supporting FIPS-201 requirements.
Flexible issuance processes
Choose the best process for your organisation and use case - batch production of cards either at a manufacturing facility or within your own premise. Secure card activation processes including fingerprint verification of the PIV card holder. Flexible credential replacement and renewal processes including identity re-enrolment when required.

Migrate without mass reissuance
MyID can import PIV cards issued by other systems, so agencies replacing an incumbent credential management system can take over the existing card estate and manage its lifecycle without reissuing every credential on day one.
Derived PIV credentials
Provide PIV derived credentials on mobiles, security keys & TPM protected Windows Hello for Business, issued per NIST SP800-157 at LOA-3. Includes ongoing PIV card revocation checks ensuring standards are maintained throughout the lifecycle.
Passkeys
Bring FIDO-based Passkeys into the range of credentials used in your environment, enabling a mix of different authenticators that are appropriate to your use case and compliance requirements. MyID can issue Passkeys for multiple connected Entra ID tenants, including lifecycle management of Passkeys for Entra ID issued by other solutions such as Microsoft Authenticator on mobile devices.
Physical Access Control Integration
Notify your PACS system when credentials are issued - either full PIV cards or basic access cards without certificates. Card and user status updates can flow from MyID to your PACS, synchronising physical and logical access.
Air-gap deployment
100% offline credential lifecycle operations. No cloud dependency, no external connectivity required, proven in classified and air-gapped environments.
Integrations for federal PIV programmes
MyID CMS PIV builds on the integration breadth of MyID CMS, with connectors for the Certificate Authorities (CAs), HSMs (Hardware Security Modules), directories, card printers and physical access control systems that federal programmes depend on.
PACS
Card and user status updates - issuance, suspension, revocation - flow from MyID to your physical access control system through MyID's notifications web service, keeping physical access in step with credential status.
Adjudication
Support for federal adjudication workflows, including integration with the optional OPM Adjudication service - so credential issuance can be tied to the outcome of background investigations. Talk to us about your identity-proofing and adjudication requirements.
Certificate Authorities
Native connectors for Entrust, Microsoft Windows CA and PrimeKey EJBCA. APIs available for integration with additional certificate authorities. No CA lock-in, no rip-and-replace of existing PKI.
HSM support
Entrust nShield (Connect and Solo) and Thales Luna HSM support. Hardware protection for the keys MyID uses to sign and secure PIV credentials, with a dedicated integration guide for each HSM.
Active Directory, LDAP & Entra ID
Direct integration with Active Directory, LDAP directories and Microsoft Entra ID. Identity attributes drive credential issuance and lifecycle automatically. REST APIs enable integration with other identity and access management systems.
Card printers
Entrust, Fargo, XID and IDP card printer integration for PIV card production, with fully customisable card printing templates including graphical and text-based attributes and barcodes. Personalisation and printing under one workflow, one audit trail.
Common questions
Specific to federal PIV programmes. Can't find the answer? Contact our team →
MyID CMS PIV is the federal edition of MyID CMS. It adds the capabilities a federal Personal Identity Verification programme requires: FIPS 201 card issuance aligned with NIST SP 800-73, SP 800-76 and SP 800-78, PIV applet support, derived PIV credentials and PACS notifications, with 10-print biometric enrolment available through the IDMS add-ons. The underlying platform is the same; the PIV-specific capabilities and supporting documentation are the differentiator.
MyID CMS PIV helps federal agencies achieve FIPS 201-3 conformance. Cards are personalised in compliance with NIST SP 800-73 (data model), SP 800-76 (biometrics) and SP 800-78 (cryptography). Full FIPS 201 conformance spans technologies, business processes and audit requirements that go beyond any single product - talk to us about documentation to support your accreditation package.
Yes. MyID notifies your PACS when credentials are issued - either full PIV cards or basic access cards without certificates. Card and user status updates (issuance, suspension, revocation) flow from MyID to your PACS through MyID's notifications web service, synchronising physical and logical access.
MyID CMS PIV issues Derived PIV Credentials per NIST SP 800-157, binding authenticators to the user's existing PIV identity at Level of Assurance 3 (LOA-3), and is LOA-4 ready. Derived credentials can be issued to mobile devices (iOS and Android), security keys and TPM-protected Windows Hello for Business, with ongoing PIV card revocation checks maintaining standards throughout the lifecycle.
Yes. MyID CMS PIV installs entirely on your own infrastructure - on-premise or in your private cloud - and a national defence organisation deploys it across multiple air-gapped environments managing tens of thousands of end-user devices. Talk to us about the configuration considerations for running MyID without external connectivity.
MyID CMS PIV provides connectors for Entrust, Microsoft Windows CA and PrimeKey EJBCA, and multiple CAs can be connected to a single MyID instance. APIs are available for integration with additional certificate authorities. For PIV-I programmes, MyID supports issuance where certificates are provided by a CA that is cross-certified with the Federal Bridge Certification Authority, in line with the Federal PKI Common Policy Framework.