MyID MFA
Phishing-resistant authentication for the modern enterprise. MyID® MFA puts FIDO2 passkeys at the heart of multi-factor authentication, with device-bound and synced credentials that cannot be phished, replayed or intercepted. Supplementary factors are available for fallback and step-up scenarios.
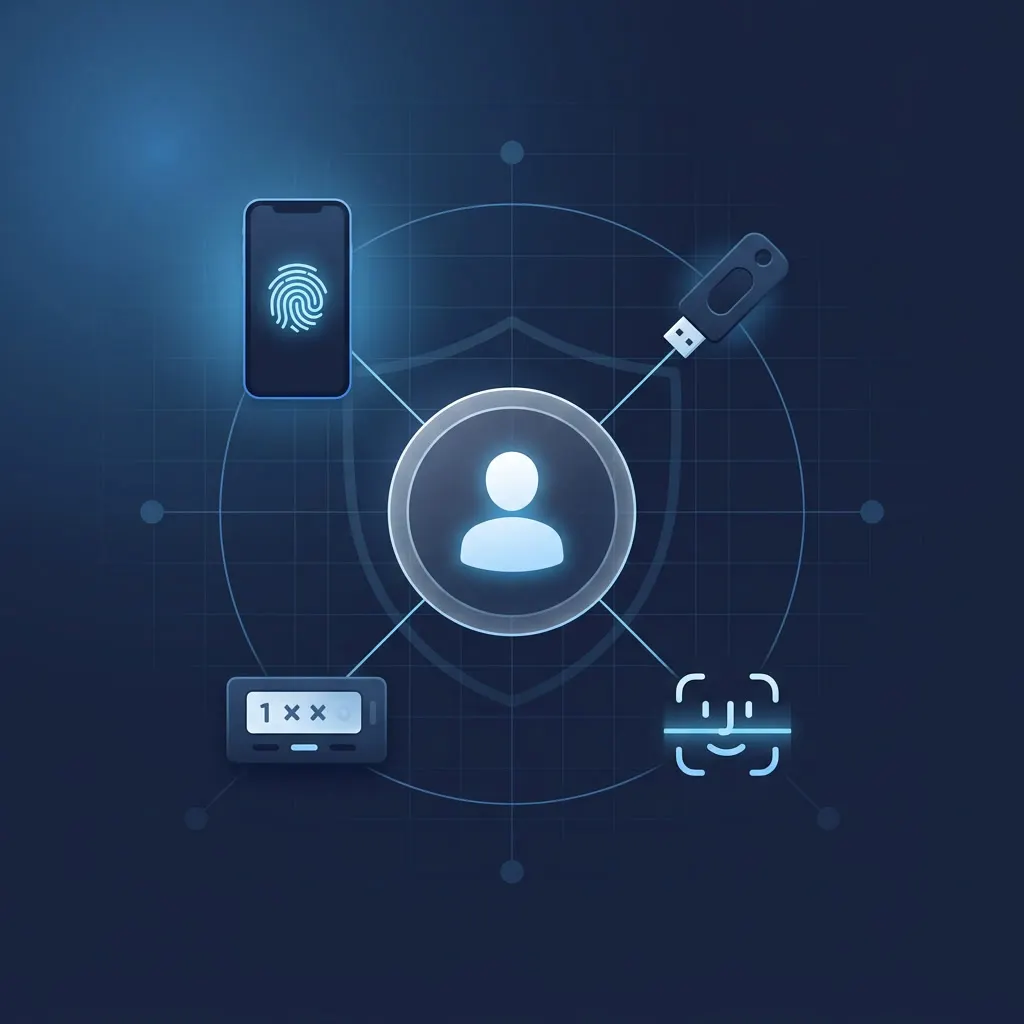
Phishing-resistant authentication, built on passkeys
MyID MFA delivers phishing-resistant multi-factor authentication for cloud, on-premise and Windows logon. FIDO2 passkeys are the primary authentication method, with device-bound and synced credentials that meet NIS2 and US Federal phishing-resistant MFA requirements. Supplementary factors are available where phishing-resistance is not required.


FIDO2 Passkeys at Enterprise Scale
Device-bound and synced passkeys as the phishing-resistant primary factor. WebAuthn - compliant, biometric-unlocked, bound to the legitimate origin. No shared secrets transmitted.
Phishing-resistant by Design
Passkeys defeat real-time phishing proxies, adversary-in-the-middle, credential replay and push bombing. Qualifies under NIS2 Article 21 and the US Federal phishing-resistant MFA mandate.
Windows Desktop Logon
Passkey-backed MFA at the Windows lock screen, online or offline. Protect workstation access, not just web apps, with the same credentials. The desktop agent can be installed on both client and server operating systems to enforce stronger authentication when accessed
Centralised Policy Engine
Mandate passkeys for high-risk groups and applications. Allow supplementary factors elsewhere. Define and enforce authentication policy by user group, device, and risk level.
Offline-Capable Architecture
Authenticate without network connectivity. Essential for air-gapped, classified and OT environments where cloud MFA cannot reach. A genuine differentiator, not a bolt-on.
Supplementary Factors Included
Push (with fatigue protection built in), OATH TOTP, YubiKey OTP, Pattern Grid and Emoji ID Grid, a simpler grid aimed at entry-level users.
Deploy the way you need to

On-Premise
Full control, no cloud dependency. Deploy on your own infrastructure with offline capability.
- Windows Server 2019+
- Active Directory integration
- 100% offline operation (client to server connectivity required at least once)
- Air-gap support

Cloud (self-managed, any platform)
Rapid deployment. Ideal for organisations moving to cloud-first security.
- Azure / AWS hosting
- Entra ID integration
- Multi-tenant support (MSP capability)
- Any cloud platform is supported

Hybrid
On-premise policy engine with cloud-managed enrolment portals. Best of both worlds.
- Mixed environment support
- Centralised policy
- Existing AD/LDAP
- Split plane architecture
Technical specifications
Authentication Server
- Windows Server 2019 / 2022 / 2025
- .NET 10 Desktop Runtime
- CPU: Quad Core 2.5 GHz (recommended)
- RAM: 8 GB (recommended)
- Active-Active HA
- 70+ Web Services API functions
Auth Methods
- FIDO2 passkeys (device-bound + synced)
- Mobile Push (with fatigue protection)
- OATH TOTP, RFC 6238
- YubiKey OTP
- OneSpan OTP
- Pattern Grid (4x4, 5x5, 6x6, 8x8; deviceless or device-bound; offline-capable)
- Emoji ID Grid - a simpler grid aimed at entry-level users
- One Time Code - One-time codes delivered by SMS or email as an additional supplementary factor for users without an app or hardware key.
Protocols and Integration
- SAML 2.0 (enterprise SSO)
- OpenID Connect
- WS-Federation
- RADIUS (built-in via NPS; FreeRADIUS also supported)
- Microsoft 365 federation
- SIEM via Windows Event Log
Desktop Agent
- Windows 10 / 11
- Windows Server 2019-2025
- Azure Entra joined accounts
- Offline logon (encrypted cache)
- Passwordless via Password Vault
- Azure Intune deployment
RADIUS Targets
- Palo Alto GlobalProtect
- Cisco VPN
- F5 BIG-IP
- Citrix Gateway
- Linux servers
- Any RADIUS-compliant device
Directory
- Active Directory (no schema changes)
- Settings stored directly in AD
- Automatic AD replication
- No separate database required
- IPv4 and IPv6 supported
Authentication that works everywhere

One-tap approval with built-in MFA fatigue protection. If a user denies a request as one they didn't make, the server automatically throttles further push requests; untrusted browser connections also require an initial offline logon

Phishing resistant passwordless authentication. Hardware-bound credentials that cannot be intercepted or replayed.
MFA without internet connectivity. Every authentication technology works offline except synced passkeys, making MyID MFA ideal for air-gapped and field environments.

Match authentication strength to the application. Set assurance levels per application and control access by AD group, IP range, logon hours, and device policy.

Protect your entire workforce in days. No infrastructure changes, no user training, no disruption to productivity.

Modern federation via SAML 2.0 and OpenID Connect, plus RADIUS and ADFS for existing infrastructure, and a REST API for everything else. Protect legacy and modern applications from a single platform.

Users enrol and manage their own authenticators - Authenticator app, OATH, YubiKey, OneSpan Digipass and FIDO/passkey - through the Self Service Portal.

Grid Pattern: deviceless or device-bound - Grid Pattern works with or without a device, supports sizes up to 8×8, and an administrator can register a grid on a user's behalf - useful for offline and assisted-enrolment scenarios.
Common questions
Everything you need to know. Can't find the answer? Contact our team →
MyID MFA delivers phishing-resistance through FIDO2 passkeys, both device-bound (hardware keys, mobile devices) and synced. Each passkey uses WebAuthn challenge-response and is cryptographically bound to the legitimate origin. A real-time phishing proxy or adversary-in-the-middle attack cannot steal a usable response because there is no code or shared secret to intercept - only the legitimate origin can complete the challenge.
Yes. MyID MFA Pattern Grid is one offline multi-factor authentication with no network connectivity, no OTP expiry and no dependency on a mobile device. This is among the few commercially available offline MFA methods and is critical for classified, air-gapped and remote-working scenarios.
MyID MFA supports a broad range of authentication methods. FIDO2 passkeys — device-bound and synced — are the phishing-resistant primary factor, backed by supplementary factors for fallback and step-up: mobile push (with fatigue protection built in), OATH TOTP (RFC 6238), YubiKey OTP, OneSpan Digipass OTP, Pattern Grid (deviceless or device-bound), Emoji ID Grid for entry-level users, and one-time codes delivered by SMS or email. Every method except synced passkeys works offline after an initial online logon.
MFA fatigue attacks flood users with push notifications until they accept. MyID MFA combats this through push rate throttling further push requests; untrusted browser connections, and by offering FIDO2 passkeys as the phishing-resistant primary factor - removing push entirely for high-risk users.
Yes. MyID MFA federates with Microsoft 365 and Entra ID via SAML 2.0 (no ADFS required) and supports Entra joined user accounts through the Windows Desktop Agent. MyID MFA issues and manages FIDO passkeys entirely independently of Entra - it's a standalone FIDO server that runs on-premise or in the cloud.
MyID MFA meets NIS2 Article 21 Advanced Authentication, NIST SP 800-63B AAL3 with FIDO2 device-bound passkeys (AAL2 with synced passkeys, also phishing-resistant), CJIS Security Policy 5.6.2.2 and PCI-DSS v4 MFA requirements. For FIPS 201 (PIV) credential management, pair MyID MFA with MyID CMS or MyID PIV. Our compliance team can provide evidence packs for audit purposes.
Trusted at every scale, in every environment
Intercede has specialised in digital identity management since 2001. Our engineering team holds deep expertise in PKI, FIDO2, smart card systems, and credential lifecycle management across government, defence, and enterprise environments.
MyID is deployed in environments requiring FIPS 201, NIS2, NIST SP 800-63B and ISO 27001. Intercede itself holds ISO 27001 and Cyber Essentials Plus certification.
From a single government department to national identity programmes serving millions of citizens, MyID is proven at every scale. A major US federal agency runs MyID CMS for its entire 47,000-person workforce.